Ruijie
RG-WALL 1600-Z3200-S
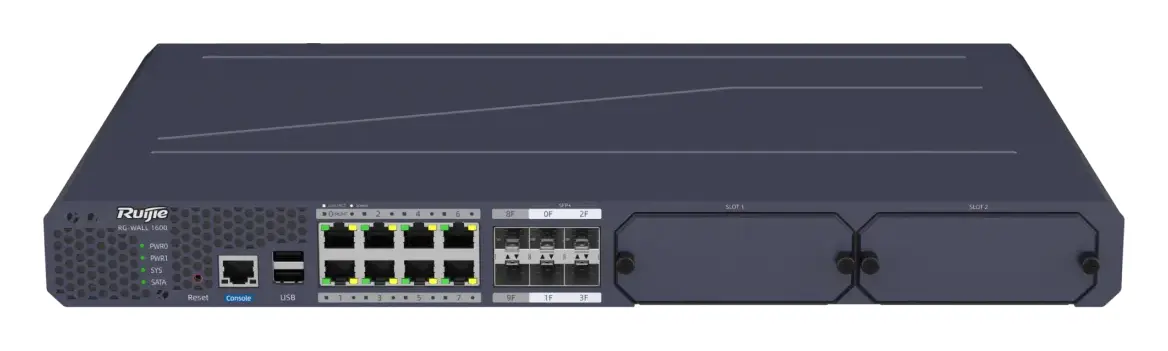
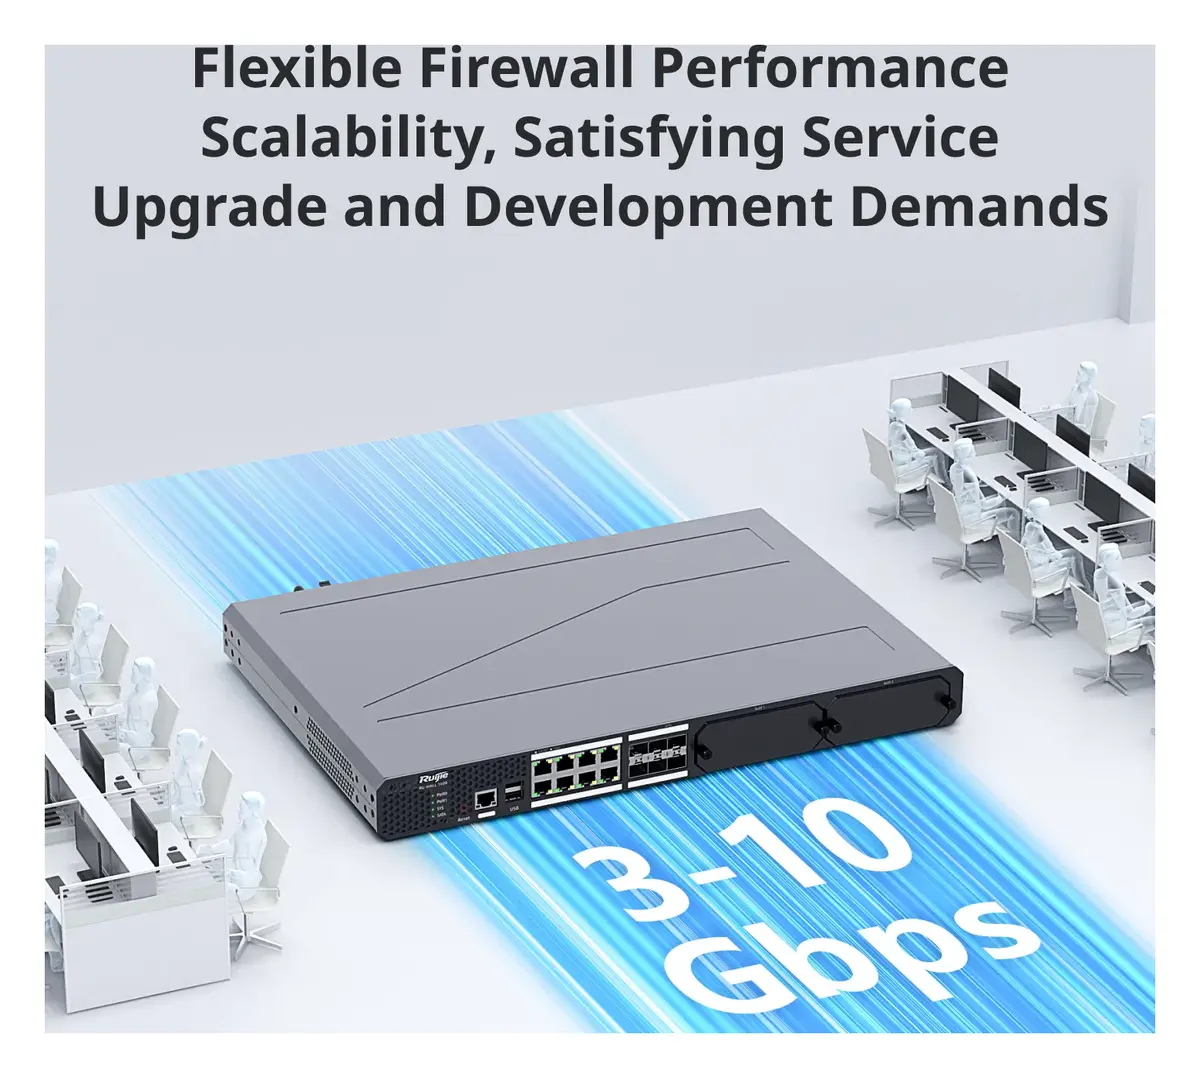
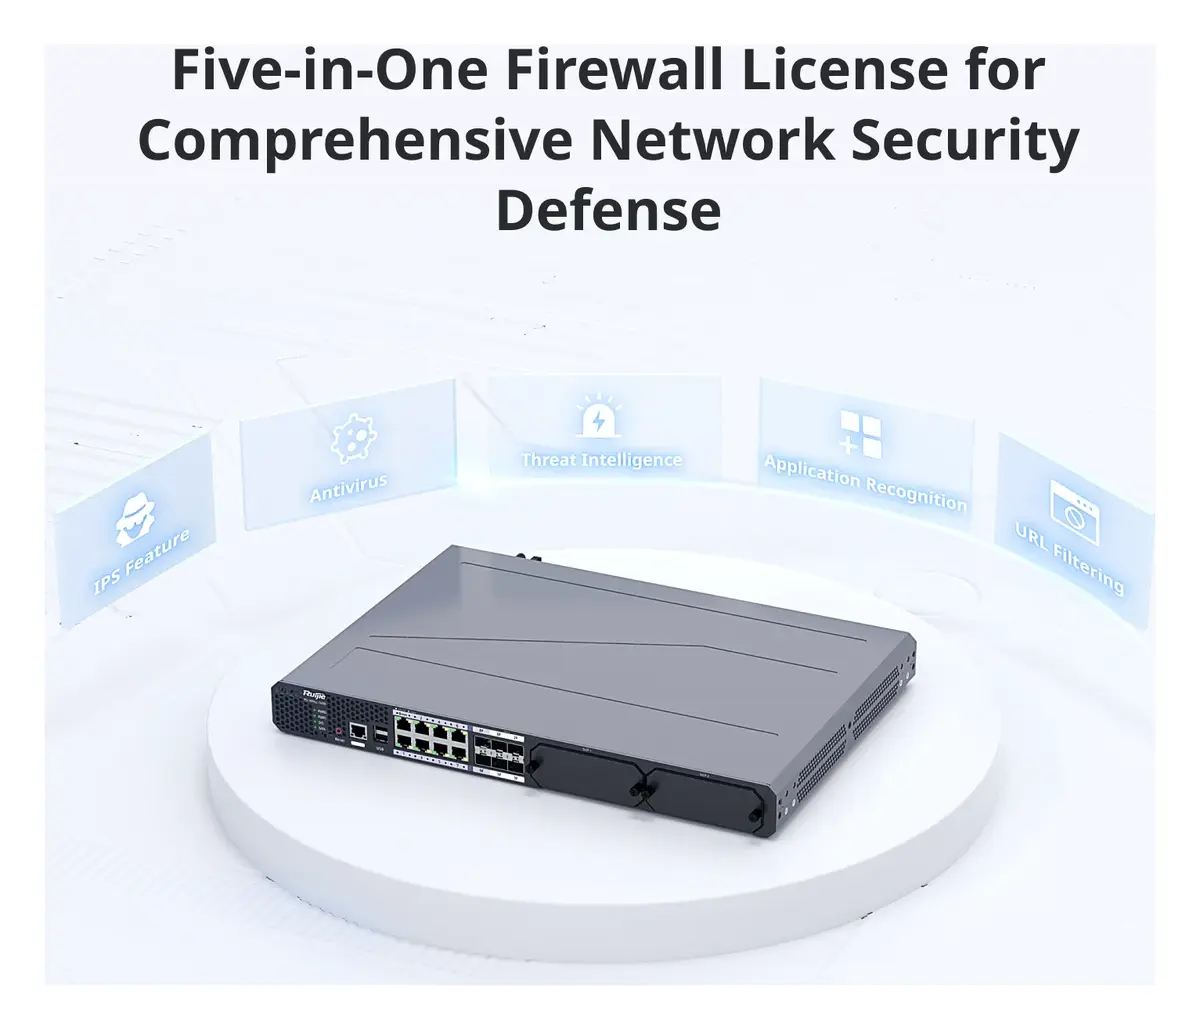
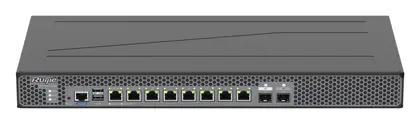
RG-WALL 1600-Z5100-SRuijie RG-WALL 1600-Z5100-S firewall: License-based scalability, firewall throughput scaling up to 10 Gbps, Five-in-one firewall license, comprehensive network security defense capability, Cloud, make your business easy, Intelligent policy manager ( port scan + traffic learning), simple firewall d.
Adet ve proje bilginize göre güncel fiyat, stok ve teslim süresini iletelim.
Üretici veri sayfasından derlenmiştir; proje öncesi güncel datasheet ile teyit edilmesi önerilir.
| Firewall Throughput4 - Firewall (Traffic Mix) | IPS1; NGFW1,2; Threat Protection1,3 |
|---|---|
| 15 Gbps - 3 Gbps | 1.8 Gbps; 1.6 Gbps; 1 Gbps |
| 15 Gbps - 4 Gbps | 2.1 Gbps; 1.7 Gbps; 1.14 Gbps |
| 15 Gbps - 5 Gbps | 2.4 Gbps; 1.8 Gbps; 1.28 Gbps |
| 15 Gbps - 6 Gbps | 2.7 Gbps; 1.9 Gbps; 1.42 Gbps |
| 15 Gbps - 7 Gbps | 3 Gbps; 2.1 Gbps; 1.56 Gbps |
| 15 Gbps - 8 Gbps | 3.3 Gbps; 2.2 Gbps; 1.7 Gbps |
| 15 Gbps - 9 Gbps | 3.6 Gbps; 2.3 Gbps; 1.8 Gbps |
| 15 Gbps - 10 Gbps | 4 Gbps; 3.5 Gbps; 2 Gbps |
| Firewall throughput of IPv4 packets (1518-byte UDP packets)4 | 15 Gbps |
|---|---|
| Firewall throughput (packets per second) | 2.3 Mpps |
| Concurrent sessions (TCP) | 1000000 |
| New sessions/second (TCP) | 134000 |
| Firewall policies | 4000 |
| SSL VPN throughput (1392-byte) | 3 Gbps |
| Concurrent SSL VPN users (recommended maximum, tunnel mode) | 1000 |
| Application control throughput (HTTP 64K); 2 | 10 Gbps |
| IPsec VPN throughput (512-byte) | 4 Gbps |
| Gateway-to-Gateway IPsec VPN Tunnels | 1000 |
| Ürün Boyutları (G x D x Y) | 440 mm x 300 mm x 43.6 mm (17.32 in. x 11.81 in. x 1.72 in.) |
|---|---|
| Kutu Boyutları (G x D x Y) | 545 mm x 450 mm x 130 mm (21.46 in. x 17.72 in. x 5.12 in.) |
| Ürün Ağırlığı | 4.44 kg (9.79 lbs) |
| Kutulu Ağırlık | 5.7 kg (12.57 lbs) |
| Form Faktörü | 1 RU rack |
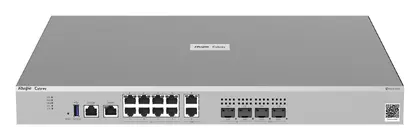
| Sabit Servis Portları | 8 x 10/100/1000BASE-T ports; 2 x 1GE SFP ports; 4 x 10GE SFP+ ports |
| Sabit Yönetim Portu | 1 x RJ45 MGMT port (reusing Ge0/0); 1 x RJ45 console port (RS-232) |
| USB Portu | 2 x USB 2.0 ports |
| Disk | No hard disk for factory delivery. A 1 TB SATA hard drive can be added.; To ensure syslog security and system stability, please use Ruijie brand hard drives. Ruijie will not be responsible for any syslog loss or performance degradation resulting from the use of third-party hard drives. |
| Konnektör Tipi | SATA |
| Memory Capacity | 1 TB |
| Hard Disk Type | Hard disk drive |
| Maks. Güç Tüketimi | 14 W |
| Çalışma Nemi | 5% to 90% RH (non-condensing) |
| Depolama Sıcaklığı | –40°C to +65°C (–40°F to +149°F) |
| Depolama Nemi | 8% to 90% RH (non-condensing) |
| Rakım | Operating altitude: 0 m to 3,000 m (0 ft. to 9,843 ft.) |
| Hot Swapping of Hard Disk | Desteklenmiyor |
| Ağırlık | 0.300 kg (0.661 lbs.) |
| Güç Kaynağı | 2 x pluggable power modules (one power module for factory delivery); l Rated input voltage: 100–240 V; 50–60 Hz; l Rated input current: 2 A (maximum) |
|---|---|
| Maks. Güç Tüketimi | < 60 W |
| Çalışma Sıcaklığı | 0°C to 45°C (32°F to 113°F) |
|---|---|
| Depolama Sıcaklığı | –40°C to +70°C (–40°F to +158°F) |
| Çalışma Nemi | 40% RH to 65% RH (non-condensing) |
| Depolama Nemi | 10% RH to 90% RH (non-condensing) |
| Gürültü Seviyesi | 36 dB |
| Çalışma Rakımı | 0–5000 m (0–16404 ft.) |
| Uyumluluk | EMC SZEM2404002506ATV; LVD SZES2404002242AT |
| Ağ | RG-WALL 1600-Z-S Series |
|---|---|
| Physical interface | Configuring interfaces as LAN/WAN interfaces; three modes for WAN interfaces: PPPoE, DHCP, and static IP; configuring the routing, transparent, or bypass mode for interfaces; configuring secondary IP addresses for LAN interfaces in routing mode |
| Sub-interface | Configuring sub-interfaces and VLAN IDs |
| Bridge interface | Configuring interfaces in transparent mode as bridge interfaces |
| Aggregate interface | Configuring aggregate interfaces |
| Yönlendirme | IPv4/IPv6 static and dynamic routing, routing policy, Policy-based Routing (PBR), ISP address library-based routing, application-based routing, and egress load balancing |
| DHCP server | DHCP server functions |
| DNS server | Configuring DNS addresses for devices |
| DDNS | Multiple DDNS service providers supported |
| Link detection | Link detection and link detection logs |
| VPN | SSL VPN, IPsec VPN, PPTP, and L2TP |
| VRRP | VRRP functions |
| High availability | Deployment with redundancy to achieve automatic switchover between active and passive devices, ensuring service continuity |
| Object | RG-WALL 1600-Z-S Series |
| Address and address group | Configuring IPv4/IPv6 address objects in IP address/range format |
| Zone | Configuring security zones |
| Application and application group | Configuring application types in application/application group mode |
| Service and service group | Configuring service objects; common default port services supported |
| Time plan | Configuring time objects; one-off time plans and cyclic time plans supported |
| ISP address library | Default ISP address libraries: China Telecom (CHN), China Mobile (CHN), China Unicom (CHN), CERNET (CHN), and Beijing Teletron (CHN); customizing, importing, and exporting ISP address libraries |
| Virus protection template | Configuring content object templates; antivirus (AV) templates supported; configuring quick scan or deep scan; configuring templates based on protocols and directions; setting excluded viruses |
| Intrusion prevention template | Configuring content object templates; predefined Intrusion Prevention System (IPS) templates supported; customizing IPS templates; configuring rule filters based on objects, severity, protocols, and threat types; setting excluded rules |
| File filtering | Configuring content object templates; file filter templates (filtering by file type) supported |
| SSL proxy certificate | Adding, importing, deleting, viewing, and downloading SSL proxy certificates; configuring a global SSL proxy certificate |
|---|---|
| Server certificate | Importing, deleting, viewing, and downloading server certificates |
| Security rule base | Viewing default security rules in the IPS security library |
| Content identification | URL category and keyword configuration |
| User authentication | User management, user import, authentication server configuration, real-name user information synchronization, and authentication policy configuration |
| Policy | RG-WALL 1600-Z-S Series |
|---|---|
| Traffic learning | Traffic learning to record destination IP addresses and port numbers as well as abnormal traffic; exporting traffic learning logs |
| Network address translation (NAT) | NAT; configuring NAT policies; importing NAT policies in a batch; common NAT application-level gateway (ALG) services; server port mapping; viewing NAT address pool status |
| Security policy | Configuring security policies; customizing policies based on parameters including objects, contents, and zones; viewing the policy list; importing security policies in a batch |
| Policy simulation | Simulating policy execution in the simulation space to check whether uncertain security policies can achieve expected effects |
| Policy configuration wizard | Security policy configuration wizard for conducting port scan, performing configurations, testing configurations, and other steps to generate security policies |
| Policy optimization | Sorting out configured security policies and analyzing policies to identify redundant, expired, and conflicting policies |
| Policy lifecycle | Full lifecycle display of security policies, including detailed records of policy changes |
| Port scan | Port scan of configured IP ranges for all ports or selected ports; policy creation prompt for scan results |
| DoS/DDoS attack defense | Different DDoS attack defense policies in security defense |
| ARP attack defense | Preventing ARP attacks including ARP spoofing and ARP flooding in security defense |
| Local defense | Configuring local defense policies in security defense |
| Threat intelligence | Enabling or disabling threat intelligence; customizing threat intelligence; managing excluded threats |
| Blocklist and allowlist | Configuring global blocklists and allowlists |
| SSL proxy policy | Configuring SSL proxy policies; customizing policies based on parameters including objects, contents, and zones; viewing the policy list |
| SSL proxy template | Configuring SSL proxy templates; setting the template type to protecting client or server |
| Allowlist | Configuring domain name allowlists and application allowlists |
| Behavior analysis | Configuring analysis policies, templates, and allowlists |
| Sistem | RG-WALL 1600-Z-S Series |
| Simple Network Management Protocol (SNMP) | Connecting to third-party platforms for management through SNMPv1/v2/v3 |
| Patch installation | Downloading and installing patches for upgrade |
| Cloud management platform | Enabling or disabling unified management on the cloud management platform; log upload to the cloud |
| SD-WAN | SD-WAN networking on Ruijie Cloud |
| One-click collection | Collecting fault information with one click |
| Device health | Device health diagnosis |
| Service diagnosis | Service continuity diagnosis |
| System upgrade | System upgrade and rollback |
| Database backup | System database backup and restoration |
| Factory settings restoration | Restoring factory settings on the web UI |
Ruijie RG-WALL 1600-Z5100-S kullanım alanları ve özellikleri.
NGFW with flexible scalability, high security performance, simple configuration, cloud management, fit for network egresses of schools, SMBs, hospitals, governments, and data centers
Flexible expansion, simplified deployment, and cloud O&M, fully unleashing security defense capability
* To ensure syslog security and system stability, please use Ruijie brand hard drives. Ruijie will not be responsible for any syslog loss or performance degradation resulting from the use of third-party hard drives.
By adding software licenses, you can increase network throughput of RG-WALL 1600-Z5100-S by 3-10 Gbps. Each software license increases the throughput by 1 Gbps. In addition, the high-performance free SSL VPN is provided, allowing up to 1000 users at no extra cost.
The five-in-one license for intrusion prevention (IPS), antivirus (AV), threat intelligence, URL filtering, and application identification enhances the network defense capabilities of your organization in an all-round way, dramatically improving the security of data and systems.
Intrusion Prevention System (IPS):
Threat Intelligence (TI):
Unmatched Protection: Ruijie's IPS signature library covers over 15,000 entries for detecting various cyber threats.
Stay Ahead of Attacks: With more than 90 classifications , including mining and ransomware, our IPS is at the forefront of security technology.
Continuous Improvement: Weekly updates and a leading number of monthly additions ensure that your network security is always one step ahead.
Millions of Signatures: Ruijie TIANMU Security Lab cooperates with a leading antivirus company and has developed over 10 million AV signatures for the Z series firewalls.
Accurate Detection: With an accuracy rate of 99.97% and a zero false positive rate , Ruijie's AV technology is widely recognized for its high precision.
TI is an important concept in cyber security and involves the collection, analysis, and dissemination of information on potential security threats from various sources. Ruijie Z series firewalls leverage a local TI signature library and employ TI for threat hunting to identify undetected threats or attackers on a network.
Comprehensive Traffic Management: Our NGFW's application control signature library can recognize 7200+ applications. With Deep Packet Inspection (DPI), the NGFW can accurately identify and control P2P traffic.
Granular Access Control: The NGFW categorizes and manages application traffic with high precision, allowing for tailored access control policies that align with your business needs.
Proactive Threat Prevention: The NGFW automatically detects and blocks malicious applications and attack payloads, safeguarding your network against emerging threats.
URL Identification: Ruijie firewall's URL signature library can precisely categorize web traffic in real time.
Secure Web Access: You can configure custom security policies to permit or deny web resource access.
Threat Interception: The NGFW detects and blocks malicious websites to prevent phishing and malware.
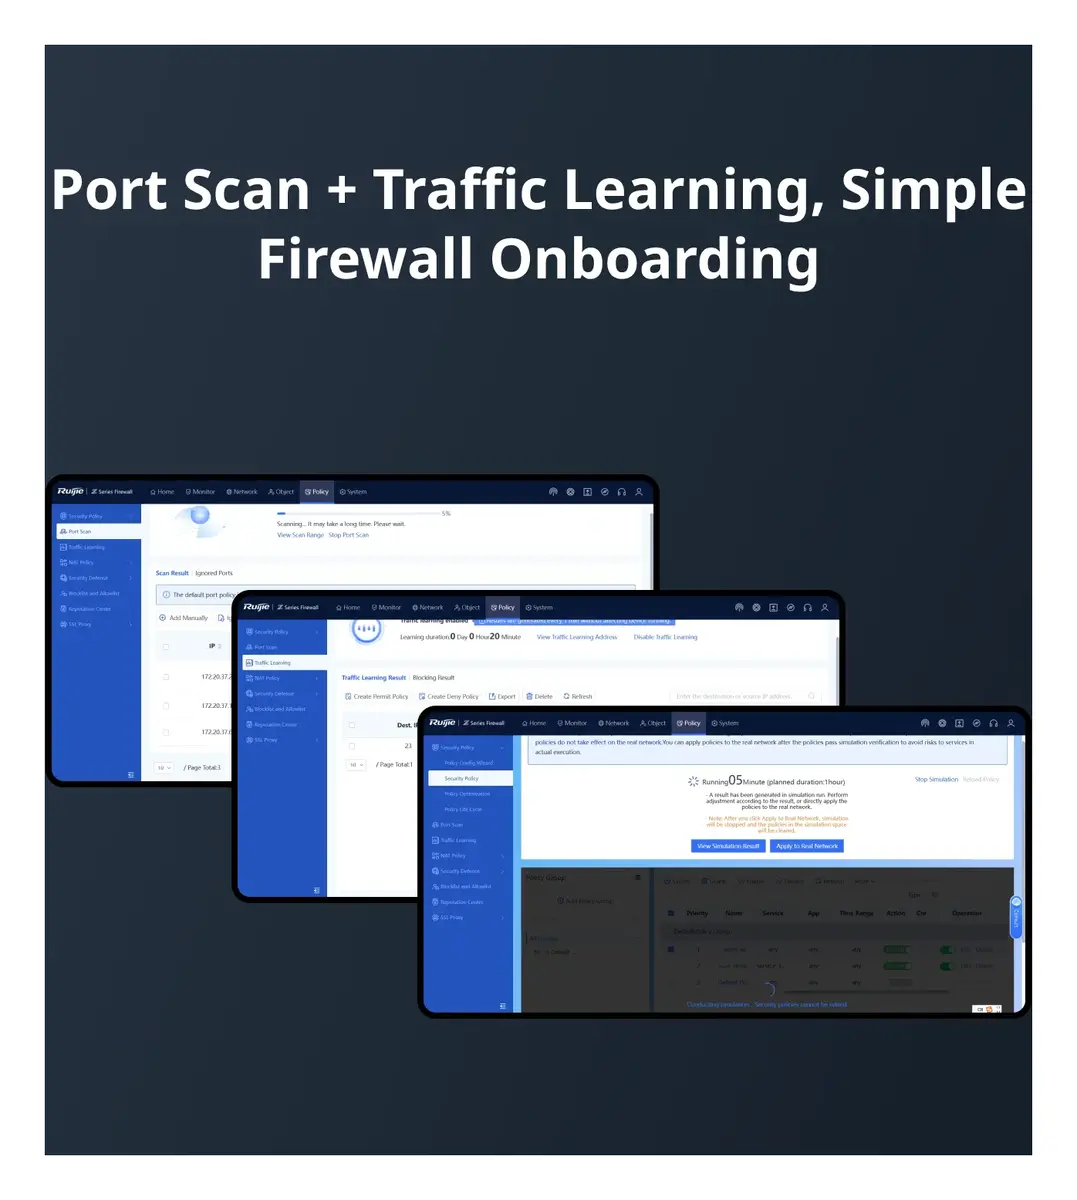
During deployment, use Port Scan to automatically identify the IP address and port number of a service system, and then enable Traffic Learning to automatically detect the service access relationship on the live network. You can also generate access control policies based on ports with one click, and complete firewall onboarding without professional knowledge.
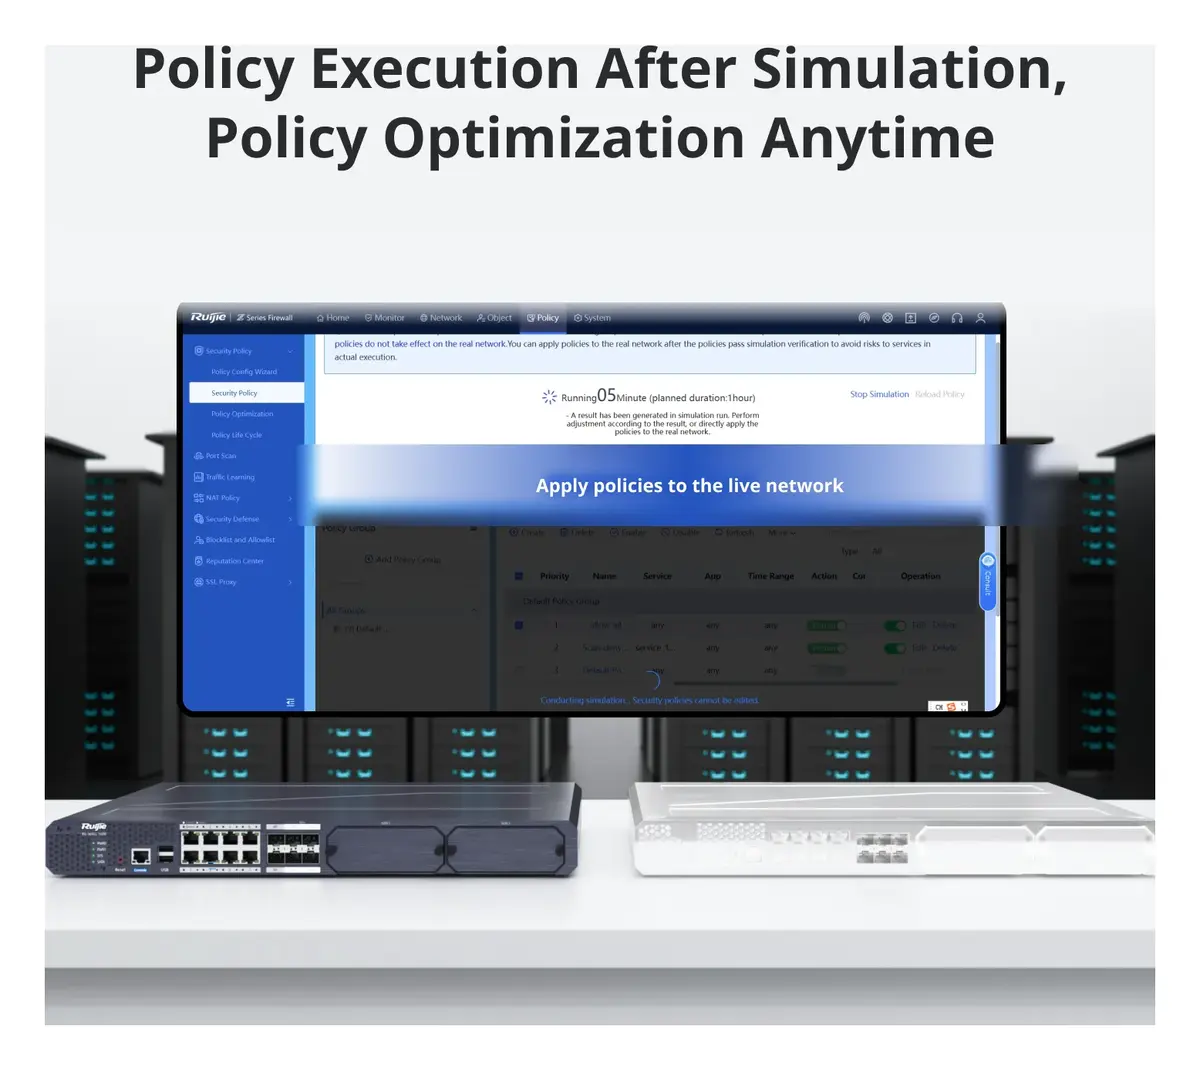
Verify policies using real traffic in Policy Simulation Space without affecting actual services or compromising network performance. Apply policies to the live network with one click after verification.
The intelligent diagnostic center supports automated analysis of network faults and provides a one-stop troubleshooting wizard for O&M personnel to quickly locate and resolve faults.
Veri sayfası ve kullanım kılavuzları.
RG-WALL 1600-Z5100-S hakkında kısa yanıtlar.
Formu doldurun, RG-WALL 1600-Z5100-S için fiyat ve teslim süresini iletelim.